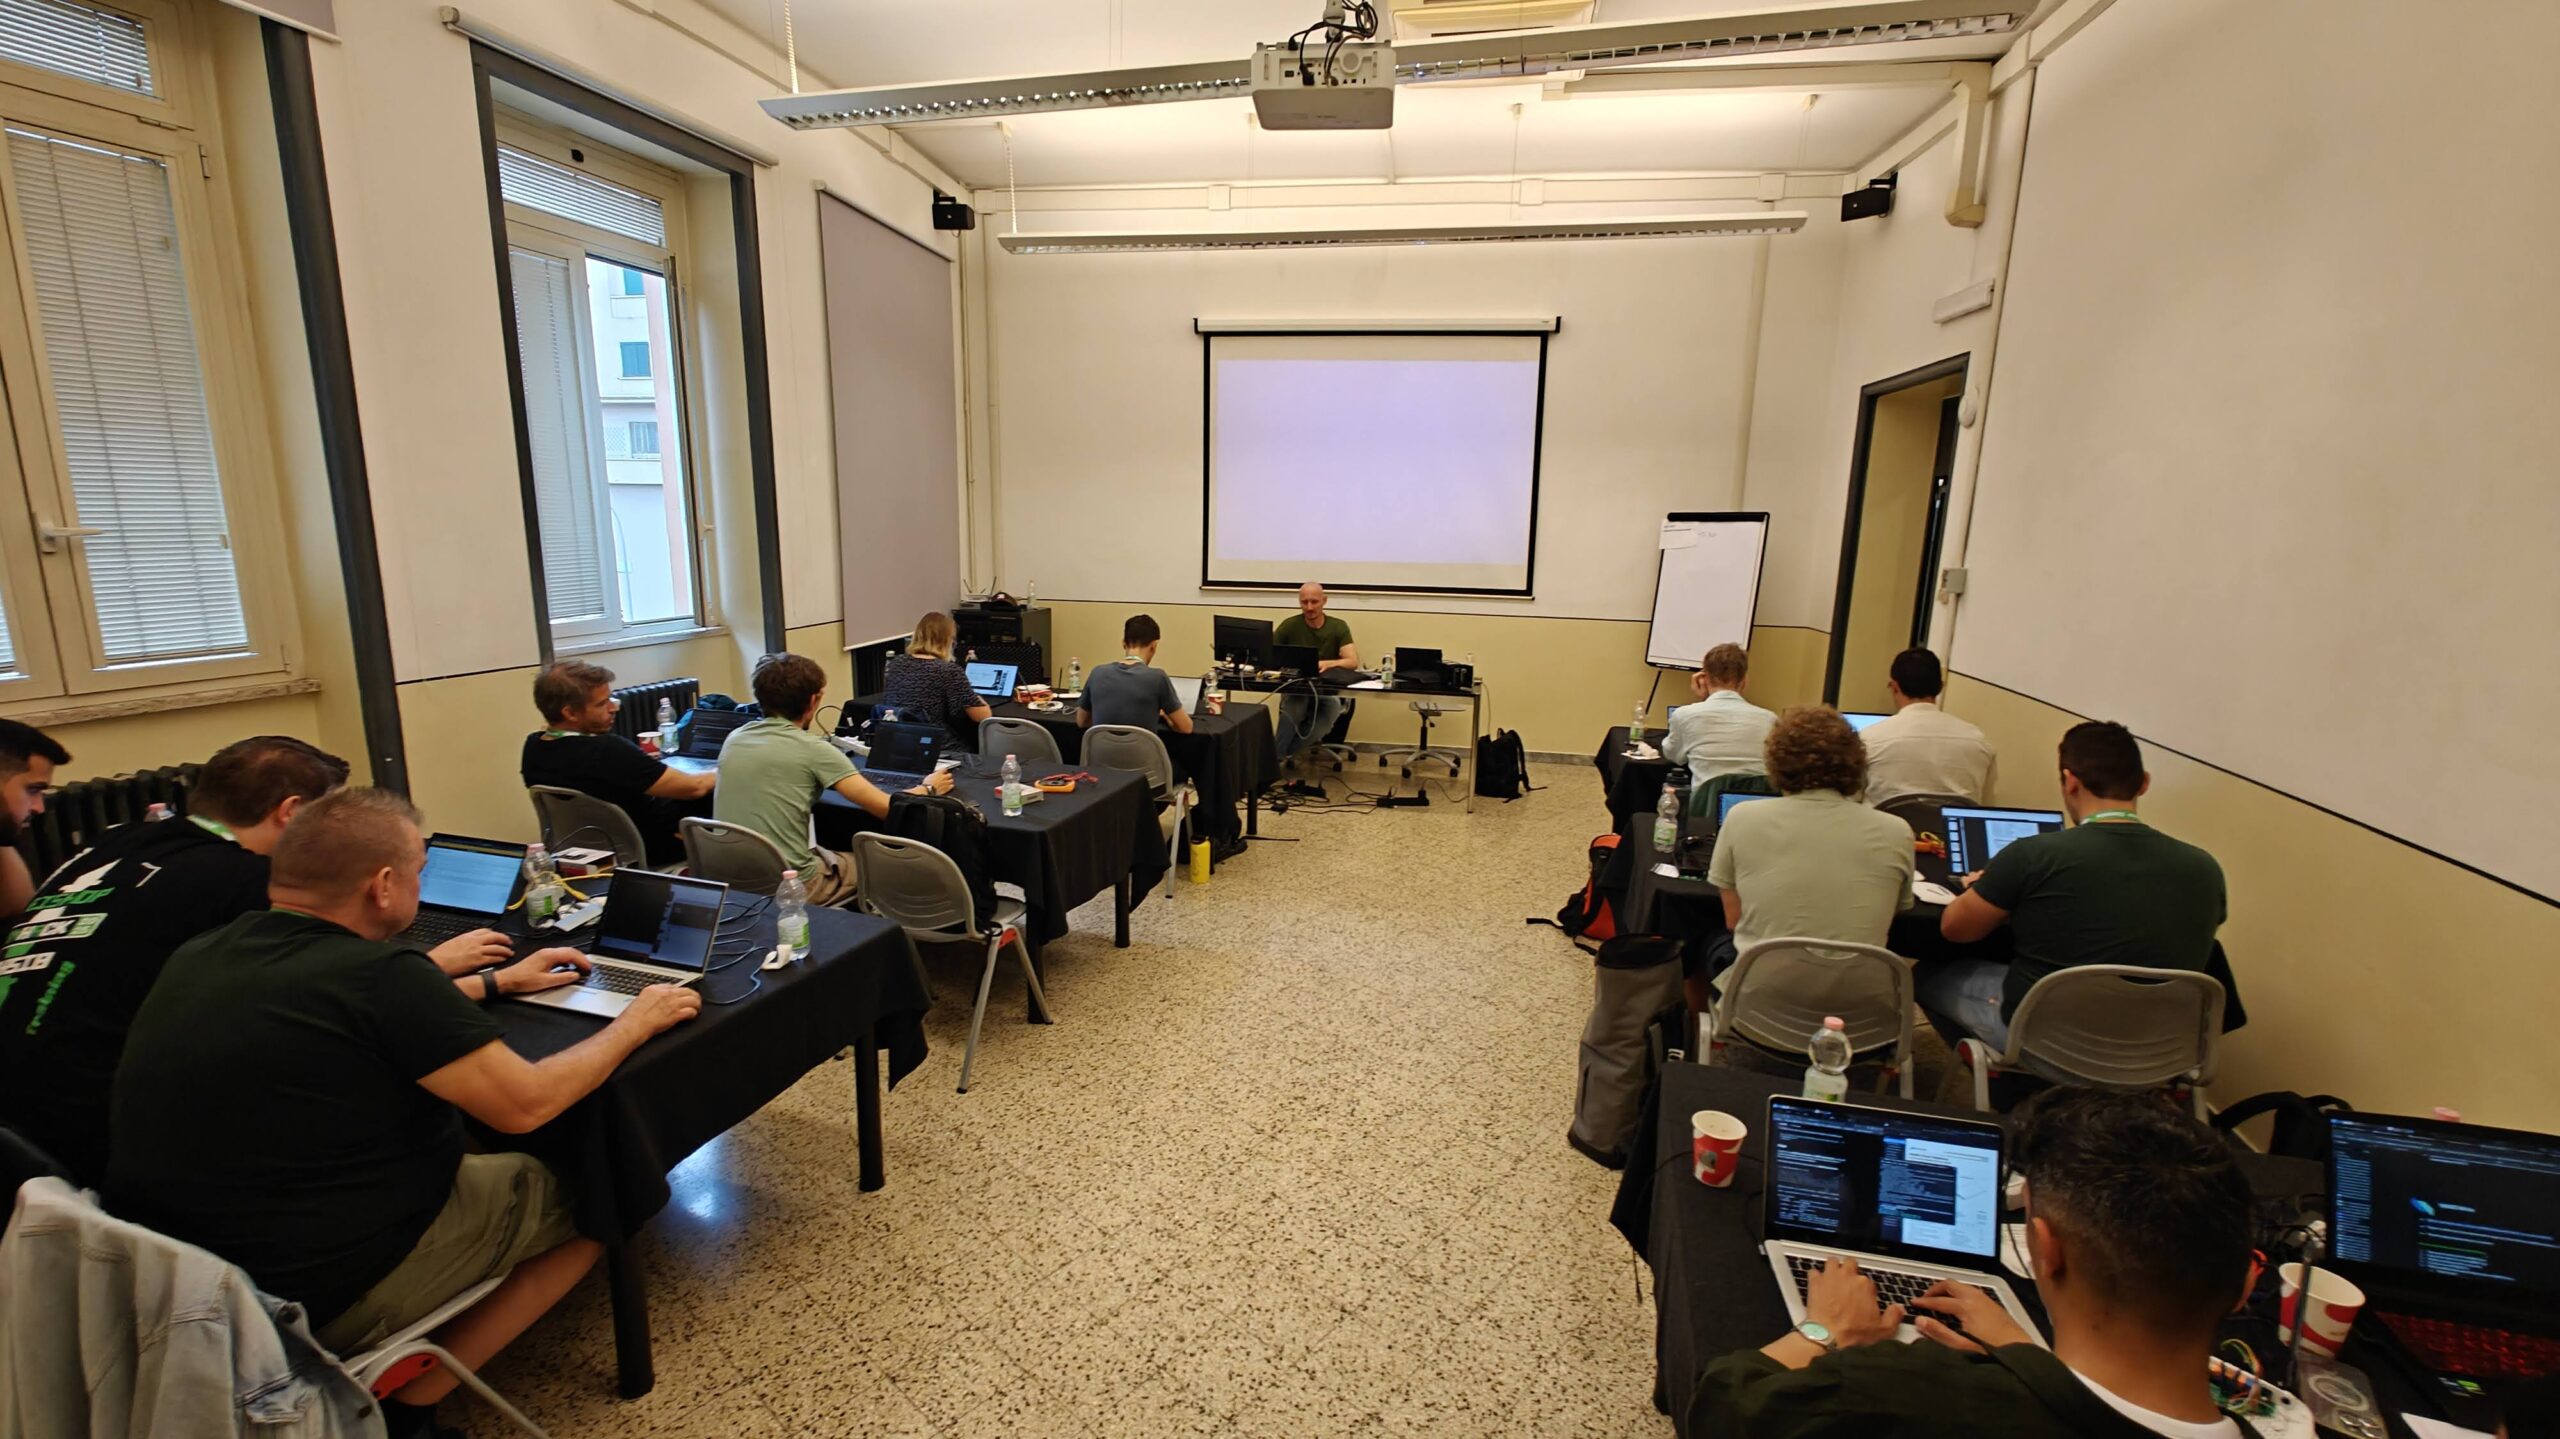

The 4th edition of RomHack Trainingarrives in Rome from September 28 to October 1, 2026. We are hosting three intensive, deep-dive technical courses at the Polo Didattico in Rome.
Go from zero to hardware hacking hero. This intensive 4-day training is a deep dive into the marvelous world of Hardware Hacking and Embedded Security. Forget just reading a book—this is a very technically-oriented, hands-on experience where you will get your hands dirty with real-world hardware.
Participants will learn the essential TTPs (Tactics, Techniques, and Procedures) used during professional security audits. From reversing PCBs and identifying “The Good, The Bad & The Ugly” debugging protocols (UART, SPI, JTAG) to dumping firmware from NAND/eMMC memories, we cover the entire hardware attack surface. By the end of the session, you’ll be able to identify, extract, and analyze firmware, performing both static and dynamic analysis to uncover vulnerabilities in the devices that surround us.
9:00 - 18:00
Master PCB reversing, firmware dumping/analysis, and hardware debugging protocols.
Security Researchers, Pentesters, and AppSec professionals curious about Hardware.
Target hardware devices, specialized hacking tools, and all necessary electronic components.
Widely regarded as the most advanced class on Windows heap exploitation, Corelan Heap doesn’t just teach you how to use known exploits—it teaches you how to conduct your own research. From precise heap folding with “Memorigami” to bypassing the latest Windows 11 mitigations, this 4-day intensive deep-dive covers the entire landscape of modern memory corruption. You will move beyond the stack to master the primary attack surface of today: the Heap.
9:00 - 18:00
Master Windows Heap internals, advanced Feng Shui, and 64-bit exploitation.
Advanced Pentesters, Vulnerability Researchers, and Exploit Developers.
Verbose courseware, custom lab VMs, and life-long post-training support.
A 4-day Linux kernel exploitation frenzy!
This training guides researchers through the field of Linux kernel exploitation. In a series of practical labs, the training explores the process of exploiting kernel bugs in a modern Linux distribution on the x86-64 architecture.
The training is structured as a series of lectures, each followed by one or more hands-on labs. The goal of each lab is to write a Linux kernel exploit following the techniques described during the lecture.
The training starts with beginner topics but proceeds into advanced areas as well. The beginner chapters include learning how to escalate privileges and bypass foundational mitigations in x86-64 kernels. The advanced chapters are primarily dedicated to the modern Slab (heap) exploitation techniques and include an in-depth analysis of the kernel allocators’ internals.
The core requirement for this training is the ability to read and write C code. Basic knowledge of the x86-64 architecture and assembly, GDB, and the common binary exploitation techniques would also come in handy. There is no need to know any Linux kernel internals: all required parts are covered during the training.
9:00 - 18:00
exploiting
linux kernel
developers
bug hunters / pentesters
slides/workbook
laboratories (VM)
Get the RomHack Camp app
To install it, tap the Share button, then “Add Magi to Home Screen”.